
Risk , Control and Compliance
A Challenge for Startups
Webinar – 08 Nov 2026
ISO 27001
Understand ISO 27001. Build a stronger information security foundation.
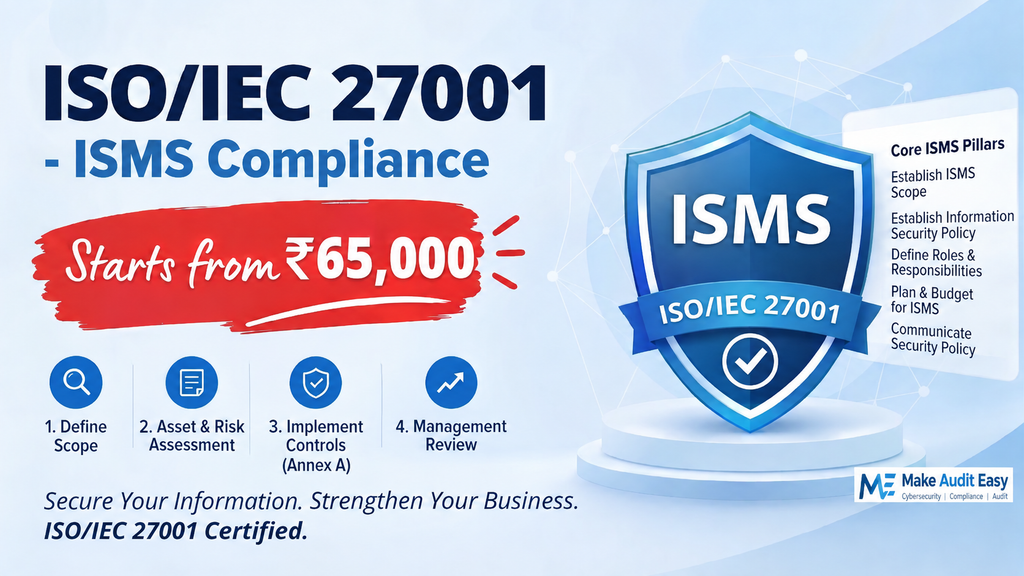
ISO/IEC 27001 is the internationally recognized standard for establishing and continually improving an Information Security Management System (ISMS). It helps organizations systematically identify risks, protect information, manage security controls, and demonstrate that information security is being managed effectively.
Explore the key requirements, ISO 27001:2022 clauses, Annex A controls, risk management process, implementation approach, audit requirements, and certification journey.
Contributor
The content published on this website is developed and reviewed with contributions from industry experts, experienced cybersecurity professionals, and recognized cyber leaders. Our contributors bring practical experience across cybersecurity, information security, risk management, compliance, audits, and ISO standards.
Our objective is to provide practical, accurate, and experience-driven knowledge that helps organizations better understand cybersecurity and compliance requirements.
Jane Roberts
Sr. Creative Designer
Hank Freeman
Web Developer
Tina Flores
UX Designer
James Scott
UX Analyst
About the MAKE AUDIT EASY
Make Audit Easy (MAE) is a cybersecurity, compliance, and audit services company helping startups, SMEs, and enterprises become secure, compliant, and audit-ready.
Our knowledge platform brings together insights from industry experts, experienced cybersecurity professionals, and recognized cyber leaders.
We simplify complex standards such as ISO 27001, SOC 2, PCI DSS, VAPT, and AI security into practical, easy-to-understand guidance.
Our goal is to help organizations build trust, meet compliance requirements, and scale with confidence.